Threat intelligence, expert analysis and practical security guidance
Insights from CREST-certified practitioners on the threats, regulations and technologies shaping cyber security.
All insights
1–12 of 164 articles
From Patchwork to Platform: Why SASE Beats a Stack of Point Solutions
Cybergen is a UK-based Cybersecurity MSSP helping SMEs stay secure with tailored services, including NIST advisory, ISO compliance, penetration testing, managed detection & response, and business continuity planning.
Read article · 8 min
Two Critical PHP Flaws: What Every Website Owner Needs to Know
Two critical PHP flaws let attackers take over web servers without a password. Learn what it means for your website and which PHP versions to update to now.
Read article · 10 min
Zero Trust Security: Why It Is Time to Retire the VPN and Rethink Access
Discover how zero trust security replaces legacy VPNs with identity based, application specific access that stops lateral movement. Expert guidance from Cybergen.
Read article · 12 min
Beyond the Questionnaire: Evidence-Based Vendor Security Assessment for Security Leaders
Vendor questionnaires create paperwork, not assurance. Learn how CISOs can tier suppliers, verify security evidence and rehearse a vendor breach before it happens.
Read article · 10 min
Approved, Warned or Blocked: A 90-Day Plan to Bring Shadow AI Under Control
Shadow AI is now the top concern for security leaders. A practical 90-day plan for CISOs to discover, classify and govern unapproved AI use without slowing the business.
Read article · 11 min
Can You Actually Restore? A Cyber Recovery Testing Playbook for Security Leaders
Backups are not a recovery plan until you have tested them under attack conditions. A practical playbook for CISOs to test, measure and evidence ransomware recovery.
Read article · 10 min
STIX and TAXII Explained: Sharing Threat Intel at Speed
What are STIX and TAXII? Learn how these open standards structure and share cyber threat intelligence, and how your SOC can use them to detect threats faster.
Read article · 9 min
How to Build a Cyber Threat Intelligence Program Your SOC Will Actually Use
A practitioner's guide to building a cyber threat intelligence program: intelligence requirements, collection, analysis, SOC integration, metrics and a roadmap.
Read article · 8 min
Your Supplier List Is Not a Resilience Plan: A Global Guide to Third-Party Cyber Risk
Learn how global enterprises can map supplier dependencies, find shared points of failure and strengthen third-party cyber risk management.
Read article · 14 min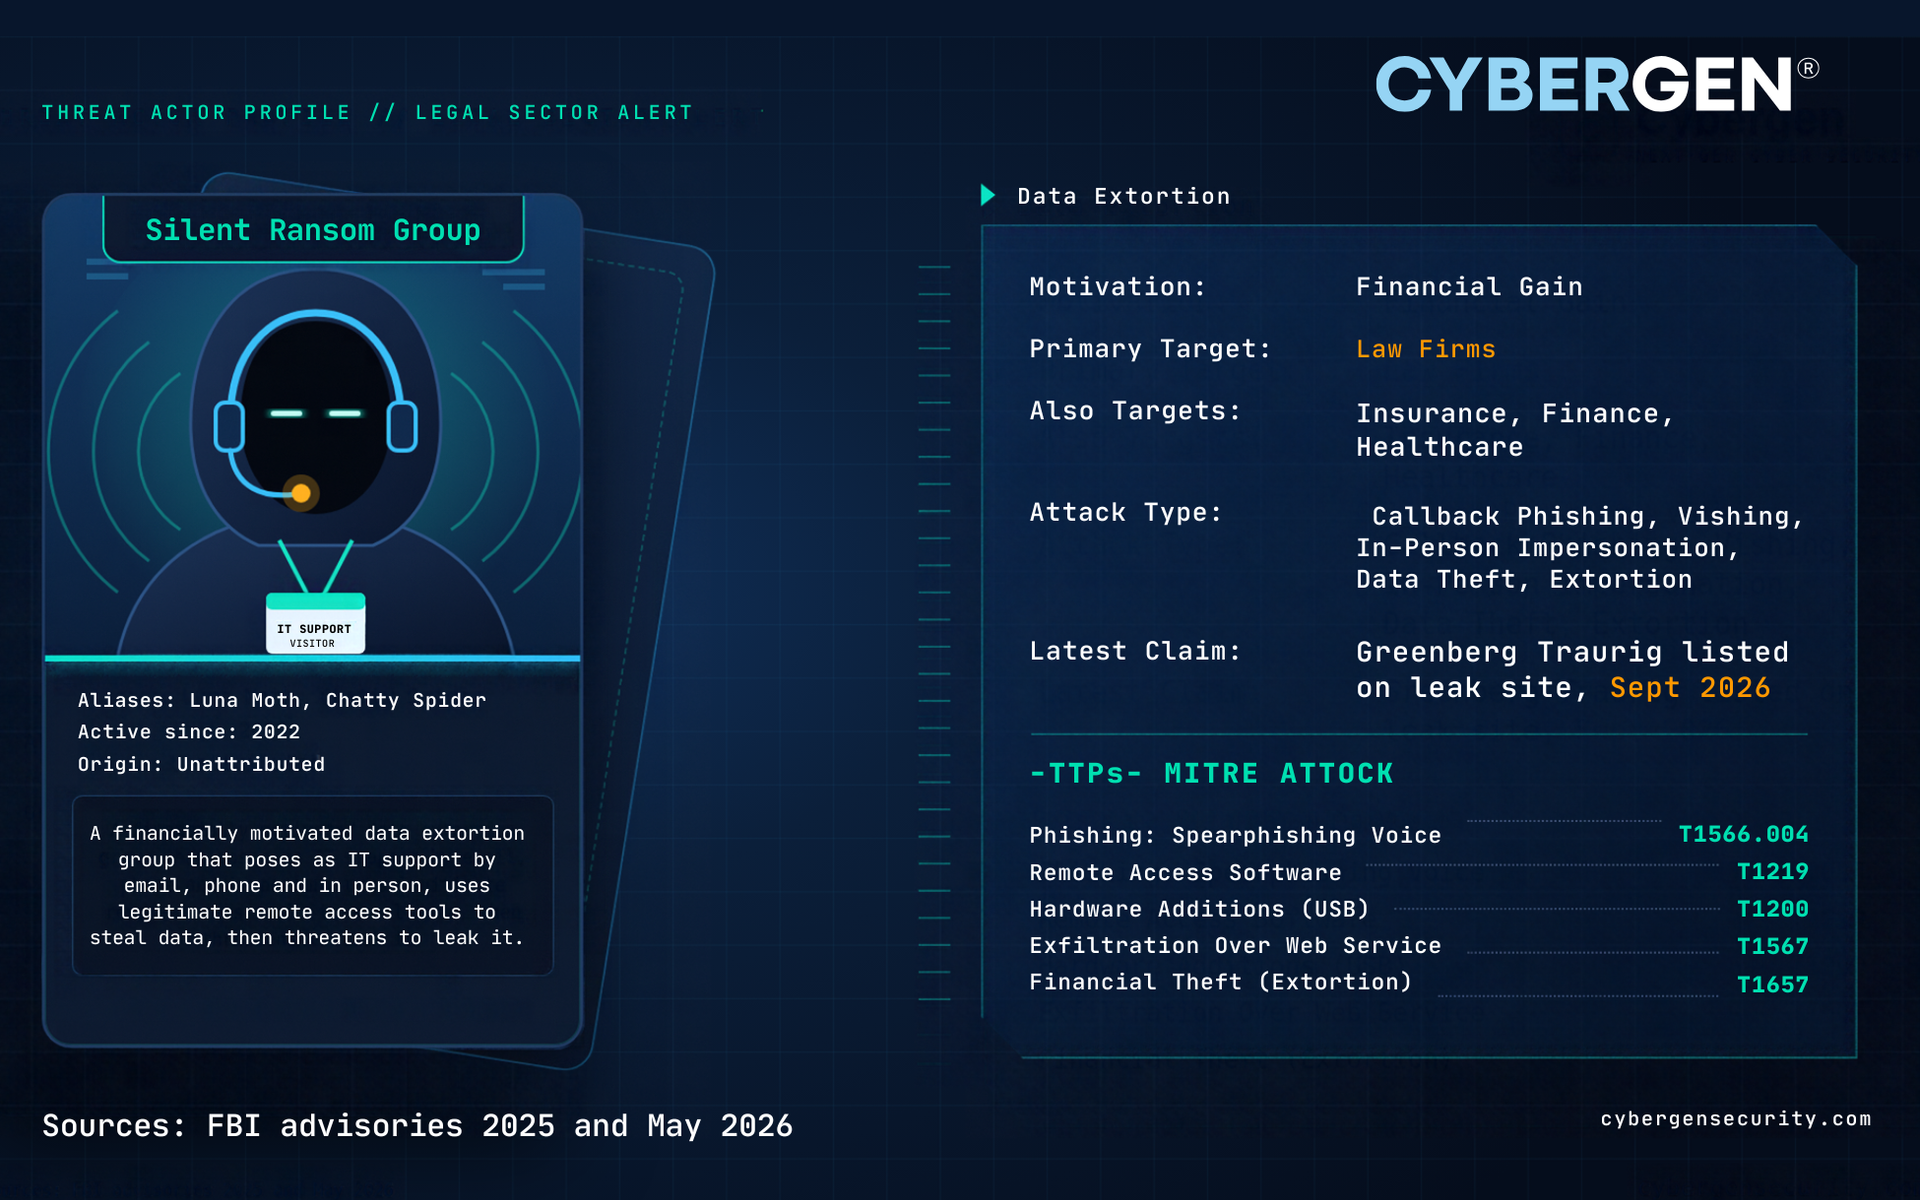
Law Firms Are Under Attack: Inside the Silent Ransom Group Threat
Greenberg Traurig is the latest law firm hit as Silent Ransom Group targets the legal sector. Learn how these attacks work and how to protect your firm.
Read article · 9 min
Non-Human Identities: The Security Blind Spot Outnumbering Your Employees 50 to 1
Non-human identities now outnumber employees by 50 to 1. Discover the risks of API keys, service accounts and AI agents, and how to secure them.
Read article · 11 min
The UK Ransomware Payment Ban Is Coming: What Public Sector and CNI Organisations Must Do Before It Becomes Law
UK ransomware payment ban explained. Discover what public sector and CNI organisations need to do now to strengthen resilience, recovery and incident response.
Read article · 11 minNo articles match that search. Try a broader term.
Get expert threat intelligence in your inbox
A monthly briefing on emerging threats, regulatory changes and practical defence advice. No spam, unsubscribe anytime.