Threat Intelligence insights
Insights from CREST-certified practitioners on the threats, regulations and technologies shaping cyber security.
Threat Intelligence
10 articles
STIX and TAXII Explained: Sharing Threat Intel at Speed
What are STIX and TAXII? Learn how these open standards structure and share cyber threat intelligence, and how your SOC can use them to detect threats faster.
Read article · 9 min
How to Build a Cyber Threat Intelligence Program Your SOC Will Actually Use
A practitioner's guide to building a cyber threat intelligence program: intelligence requirements, collection, analysis, SOC integration, metrics and a roadmap.
Read article · 8 min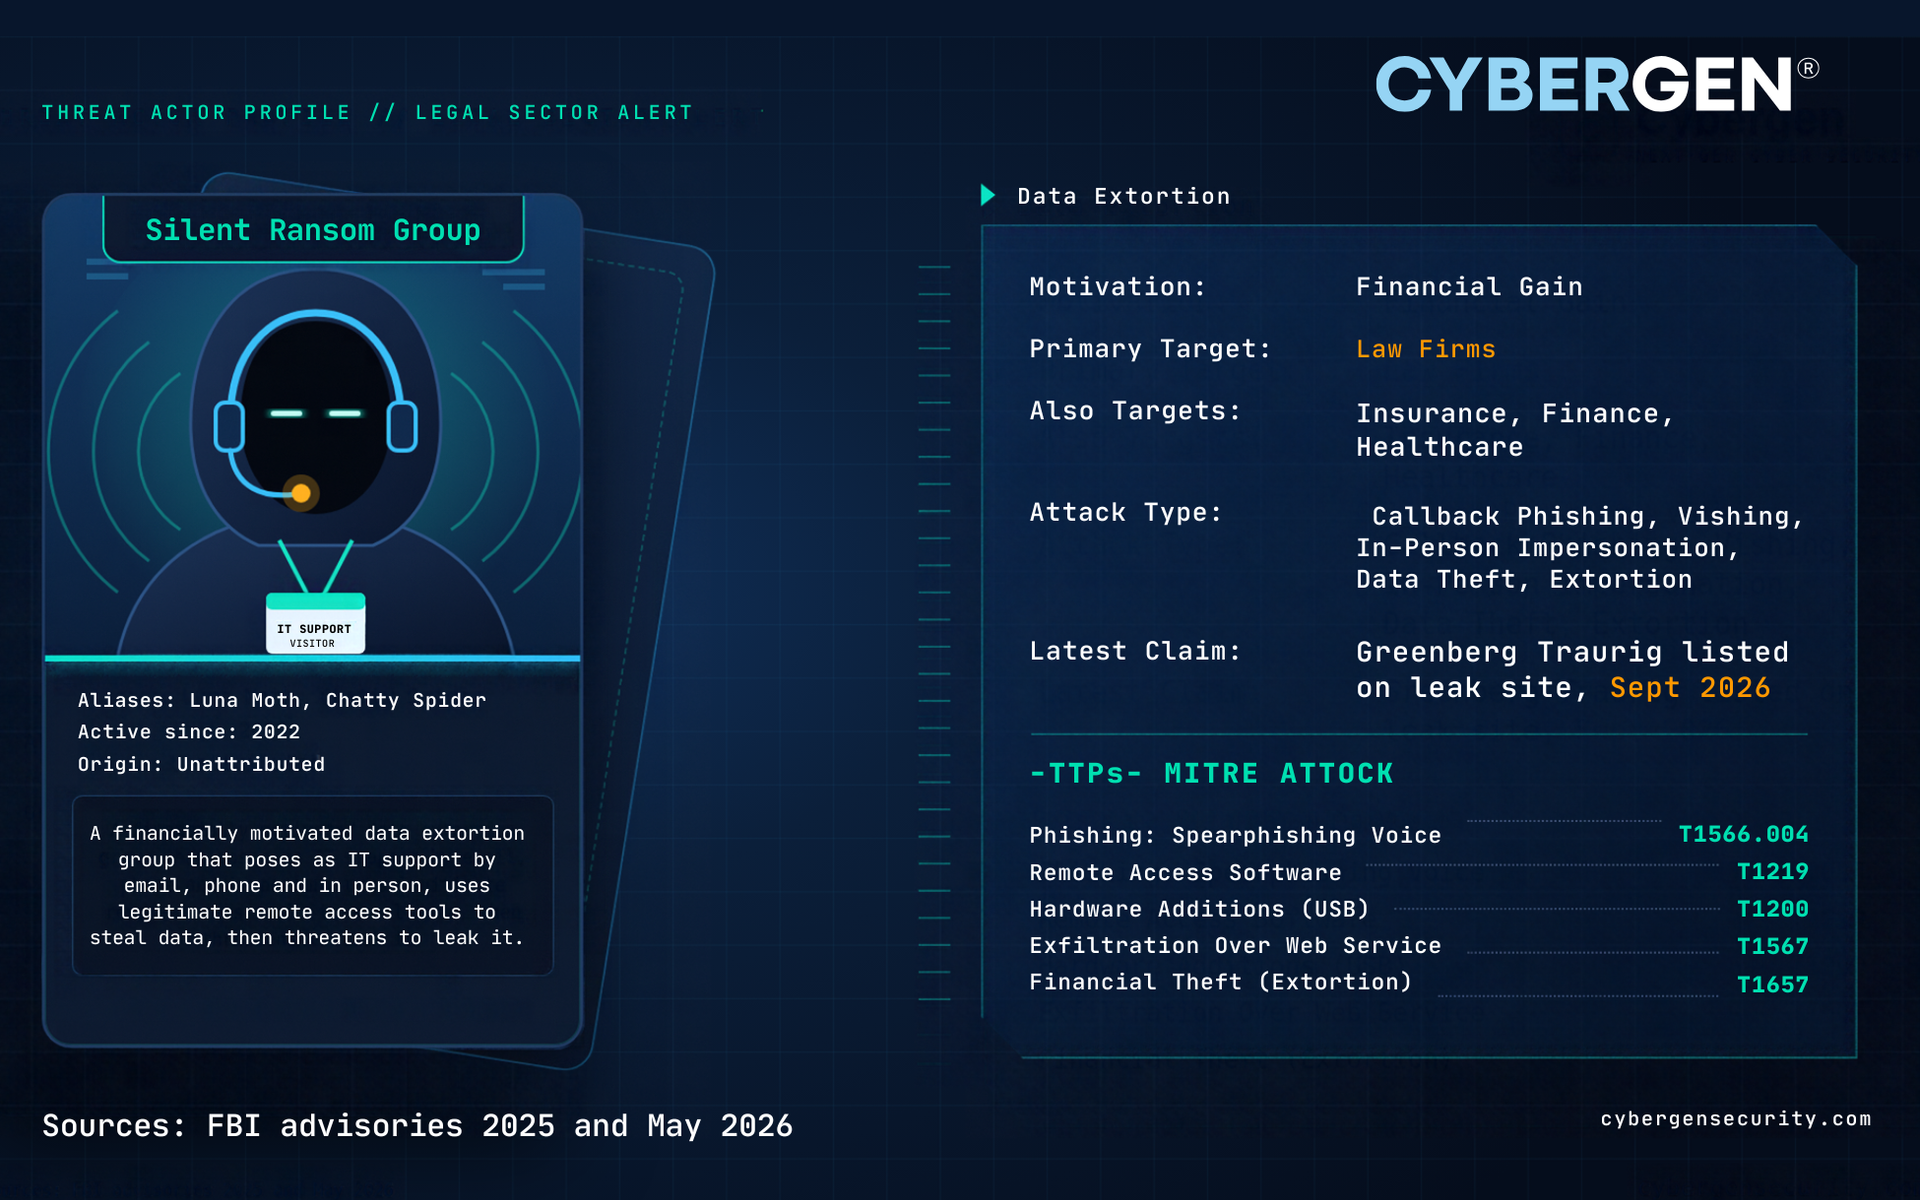
Law Firms Are Under Attack: Inside the Silent Ransom Group Threat
Greenberg Traurig is the latest law firm hit as Silent Ransom Group targets the legal sector. Learn how these attacks work and how to protect your firm.
Read article · 9 min
Why Cyber Threat Intelligence Should Drive Your Security Strategy in 2026
Learn how Cyber Threat Intelligence helps organisations reduce cyber risk, prioritise vulnerabilities, improve incident response and strengthen security in 2026.
Read article · 10 min
Why Traditional Threat Intelligence Is No Longer Enough: The Evolution of Intelligence-Led Cybersecurity
Traditional threat intelligence is no longer enough. Discover how intelligence-led cybersecurity helps organisations predict, prioritise, and prevent cyber threats before they escalate.
Read article · 14 min
Why Penetration Testing Fails (and What Good Looks Like in 2026)
Why traditional penetration testing fails in 2026, and what effective, risk-driven testing really looks like. Discover how to move beyond CVSS scores and vulnerability lists to attacker-focused attack paths, identity compromise, lateral movement, and measurable risk reduction that actually improves security outcomes.
Read article · 9 min
The Future of Cybersecurity: Navigating the Evolving Threat Landscape in 2026 and Beyond
Explore the future of cybersecurity in 2026. Discover emerging threats, evolving attack methods, and how organisations can stay resilient in a changing threat landscape.
Read article · 8 min
What Cybergen’s Threat Intelligence Reveals About How Attacks Really Start
Cyber threat intelligence reveals how modern ransomware attacks really start: credential abuse, trusted access, and quiet pre-positioning long before impact.
Read article · 8 min
The Intrusion Starts Weeks Before the Alert: What Security Teams Miss Until It’s Too Late
Most cyber attacks begin quietly with recon and stolen credentials, long before your tools alert. Learn what security teams miss and how to detect intrusions earlier with threat intel, MDR and hunting.
Read article · 12 min
Why Tiered Threat Intelligence Is the Missing Link in Modern Cybersecurity
Tiered threat intelligence turns noisy threat data into actionable insight for boards, CISOs, and SOC teams. Learn how structured intelligence enables predictive cybersecurity, strengthens MDR, and improves CTEM prioritisation.
Read article · 8 minNo articles match that search. Try a broader term.
Get expert threat intelligence in your inbox
A monthly briefing on emerging threats, regulatory changes and practical defence advice. No spam, unsubscribe anytime.