Threat intelligence, expert analysis and practical security guidance
Insights from CREST-certified practitioners on the threats, regulations and technologies shaping cyber security.
All insights · page 13
145–156 of 164 articles
Beyond the Report: The Strategic Value of Penetration Testing Documentation
Discover how penetration testing documentation goes beyond listing vulnerabilities and drives remediation, supports compliance, and informs long-term security strategy.
Read article · 11 min
API Penetration Testing: Why Traditional Methods Fall Short
Discover why traditional testing can’t protect your APIs. Cybergen’s API penetration testing helps UK businesses uncover logic flaws, secure endpoints, and meet compliance with smarter API security testing.
Read article · 20 min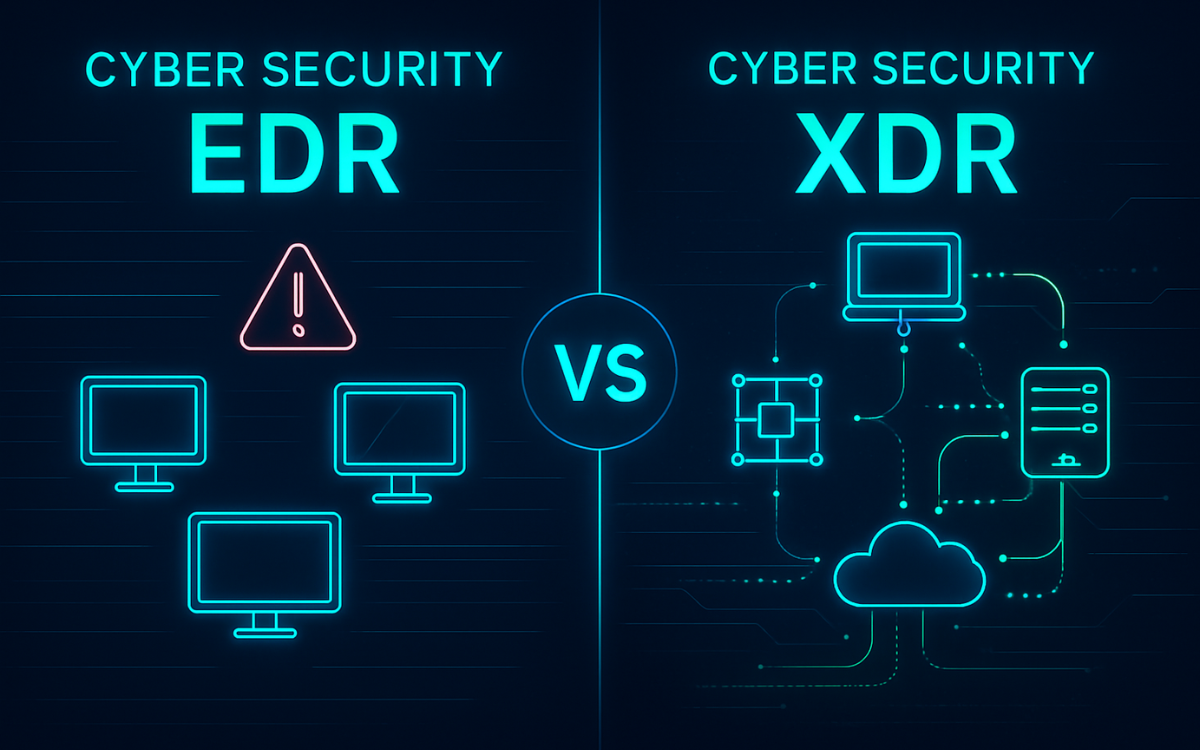
MDR vs. EDR: Which Cybersecurity Solution is Right for Your Organisation
Explore the key differences between MDR and EDR to determine which cybersecurity solution best fits your organisation’s needs. Compare features, benefits, and use cases to make an informed decision.
Read article · 13 min
ISO/IEC 27001:2022 Transition Deadline — What You Need to Know Before 31 October 2025
Learn everything you need to know about the ISO/IEC 27001:2022 transition deadline. Discover key changes, compliance risks, and how to prepare before all 2013 certifications expire on 31 October 2025.
Read article · 5 min
Every IT Environment Is Vulnerable: Why Securing Tier Zero Must Be Your Top Priority
100% of IT environments have an attack path to Tier Zero, your organisation’s most privileged assets. Learn why securing Tier Zero is essential to prevent full environment compromise.
Read article · 7 min
Vulnerability Scanning: The Cornerstone of Proactive Cybersecurity
Discover how vulnerability scanning forms the foundation of proactive cybersecurity. Learn how it helps identify risks, reduce exposure, and strengthen your organisation’s security posture.
Read article · 5 min
The Role of Manual Security Testing in an Automated World
Automation is fast, but only humans can think like attackers. Cybergen’s hybrid approach combines automated speed with manual insight to find what scanners miss and strengthen real-world defences.
Read article · 10 min
Pen Testing 101: Everything You Need to Know
This in-depth blog explains the fundamentals of penetration testing, including types of pen tests, tools, legal considerations, real-world case studies, and how it strengthens cybersecurity.
Read article · 10 min
UK Cybersecurity Overhaul: What the Cyber Security and Resilience Bill Means
Discover how the UK’s Cyber Security and Resilience Bill and GovAssure expansion will transform cybersecurity governance. Learn what your organisation needs to do to stay compliant, resilient, and ahead of threats.
Read article · 8 min
API Security in 2025: The Hidden Battlefield of Modern Digital Systems
Explore the evolving landscape of API security in 2025. Learn why business logic attacks, shadow APIs, and runtime threats demand a new approach to securing your digital ecosystem.
Read article · 7 min
A Career as a Penetration Tester: To CREST or Not to CREST
Explore the pros and cons of pursuing CREST certification for a career in penetration testing, and whether it's the right path for your professional goals in cybersecurity.
Read article · 12 min
Red Team vs. Pen Test: What's the Real Difference and When Do You Need Each?
Discover the key differences between red teaming and penetration testing, and learn when to use each to strengthen your organisation's cybersecurity posture.
Read article · 15 minNo articles match that search. Try a broader term.
Get expert threat intelligence in your inbox
A monthly briefing on emerging threats, regulatory changes and practical defence advice. No spam, unsubscribe anytime.